AI & Security: Enable Innovation Without Losing Control
AI & Security: Enable Innovation Without Losing Control
On April 16th 2026, I joined Flavio Aggio for a fireside chat at the Next IT Security C-Suite Edition in Amsterdam.
Our starting point was simple: AI is already inside our organizations. Employees are experimenting with it, teams are embedding it into workflows, and adoption is moving faster than most policies and governance frameworks can keep up with.
For security leaders, the useful question is therefore no longer “Should we allow AI?” but:
How do we enable AI safely without slowing innovation or losing control of our data and decisions?
AI is already here
Trying to solve AI adoption with a blanket ban is unlikely to work. People are already finding valuable ways to use these tools, often before organizations have decided how they want them to be used.
That makes AI another form of Shadow IT at scale.
The better response is to create simple, understandable guardrails. Be clear about what data may be shared, where approved AI services should be used and when AI-generated output needs to be validated.
The objective should be safe experimentation, not stopping experimentation.
AI is also a security capability
Much of the AI security conversation focuses on risk. That is necessary, but incomplete.
AI can also strengthen cyber defense: accelerating triage, supporting investigations, finding patterns across large volumes of information and acting as a knowledge layer for security analysts.
The principle we kept returning to was:
AI should support judgement, not replace it.
Used well, AI can help people make better decisions faster. That is different from delegating accountability or security judgement to a model.
New technology, familiar risks and some new ones
AI introduces genuinely new attack surfaces such as prompt injection, model manipulation and increasingly autonomous agent behaviour. At the same time, many familiar cyber risks are simply being amplified.
That changes what we need to test. We are no longer only testing whether code and infrastructure behave as expected. Increasingly, we also need to understand how an AI-enabled system behaves when it is manipulated, confused or pushed outside its expected boundaries.
Traditional red, blue and purple team thinking still matters, but the object being tested is changing.
Governance matters more than another tool
One of the strongest themes in our discussion was that AI security is not primarily a technology problem.
Organizations need to decide which use cases they accept, what their guardrails are, who is accountable and how much autonomy they are prepared to give AI-enabled systems.
Regulation and standards can help, but organizations that wait for regulation to tell them exactly what to do will always be behind the technology.
Compliance is the floor, not the ceiling.
Good governance should make responsible innovation easier. If governance becomes so restrictive that people work around it, it has failed.
Security is also about behaviour
People will make mistakes with AI. They will occasionally share too much information, trust an answer too quickly or use a tool in a way nobody anticipated.
Security therefore needs to assume that mistakes will happen.
A phrase I like is:
Be smart about your own stupidity.
Build environments that remain resilient when people make ordinary mistakes. Combine simple rules with training, nudges and technical guardrails instead of relying on a forty-page policy nobody reads.
Start safely, but start now
For CISOs trying to determine where to begin, our message was deliberately pragmatic. You do not need perfect control before taking the first step.
Start small. Create clear boundaries. Learn how people are actually using AI. Test the systems you introduce. Monitor what changes as workflows become more autonomous.
My three takeaways from the conversation:
- AI adoption is inevitable.
- Governance matters more than tools.
- Keep humans in control.
AI should amplify human judgement, not replace it.
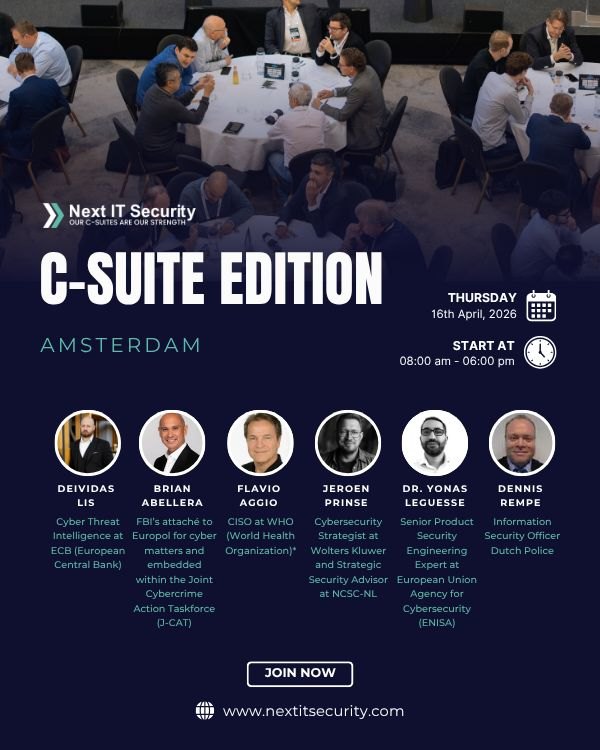
Thanks to Flavio for the open conversation and to Next IT Security for bringing together security leaders to discuss the practical realities of AI rather than only the hype around it.