The Reality of Doing More with Less
The Reality of Doing More with Less
“Do more with less” is probably one of the most repeated phrases in security.
But it can mean very different things. Sometimes it means becoming more efficient. Sometimes resources really are constrained. And sometimes it is a convenient way of avoiding a harder conversation about complexity, expectations or the things we should simply stop doing.
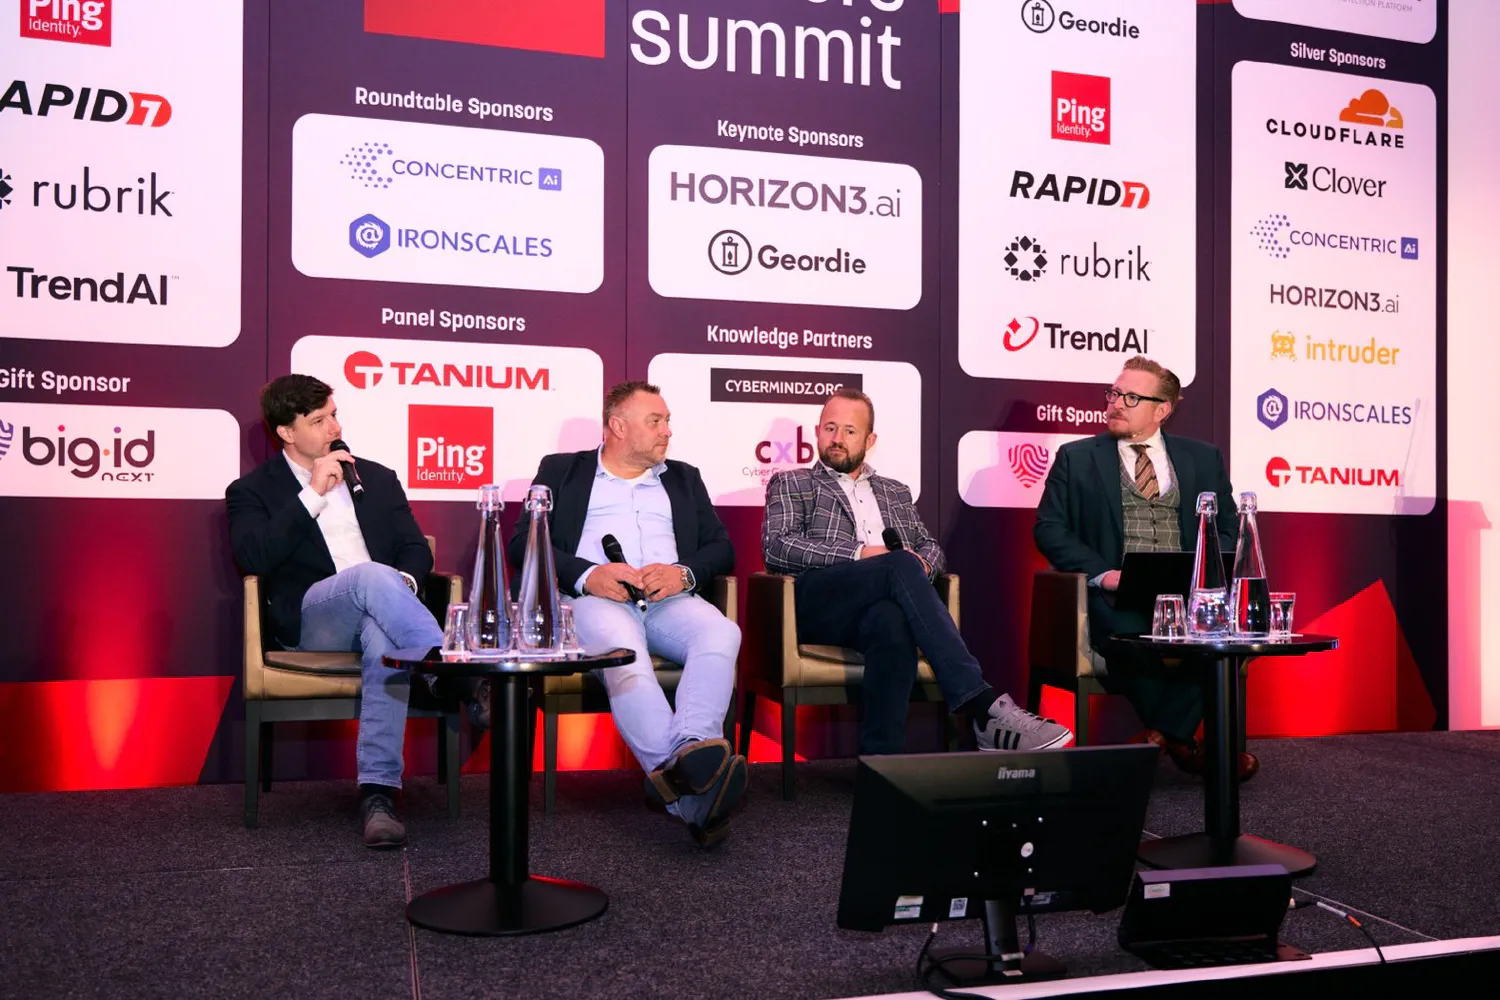
That was the tension behind the panel I moderated at the Cyber Leaders’ Summit in Antwerp.
The central question was deliberately simple:
When you cannot protect everything, how do you actually decide what deserves your people, your money and your attention?
Prioritisation means choosing
We started with reality and constraints. Plans are made with assumptions about people, budget and time. An incident has a habit of testing those assumptions very quickly.
From there, the discussion moved to prioritisation. A critical vulnerability is not automatically the most critical thing for an organisation. Severity matters, but so do exposure, business context, dependencies and the consequences of taking resources away from something else.
The difficult part of prioritisation is not deciding what matters. It is deciding what matters more.
That also means being explicit about what you choose not to fund. I wanted the discussion to get beyond principles and into those real trade-offs: what did you deliberately stop doing, and who accepted the risk that came with that decision?
Prevention meets reality
Another part of the conversation was the relationship between prevention and resilience.
You can prepare plans, run exercises and test scenarios, but an actual incident will still expose assumptions you did not know you were making. That does not make testing less valuable. It means we need to understand what testing can tell us, and where reality remains the final test.
The useful question is not whether the plan exists. It is what survives when the plan meets the incident.
Does the control actually work?
This was the part of the panel I particularly wanted to protect.
When money and capacity are tight, how do you know that the controls you continue to fund actually work?
Not that they exist. Not that they passed an audit. Not that a maturity assessment says they are implemented. Do they work, right now, in the environment they are supposed to protect?
That question becomes uncomfortable quite quickly when you follow it with:
How do you know? Tested, or assumed?
A control can meet a standard and still fail to deliver the outcome we expect from it. If we are making difficult investment decisions, evidence of control effectiveness should be part of that conversation.
A live incident can make that painfully visible: some controls turn out to have earned their budget, while others may have provided more confidence on paper than protection in practice.
Someone has to own the decision
We ended up back at leadership.
Who actually owns the decision to stop funding something? Is it an explicit choice with a named person accepting the risk, or does it happen gradually because nobody wants to make the decision?
That distinction matters. Scarcity does not remove accountability.
For me, this is where “doing more with less” becomes a much more useful conversation. Sometimes the answer is efficiency. Sometimes it is accepting risk. Sometimes it is removing complexity. And sometimes it is simply having the discipline to stop doing something that no longer matters enough.
That was also what I enjoyed about moderating this panel: moving beyond the textbook answer and into what happens when security leaders actually have to choose.